For developers shipping agent-written code
Know when a release is safe to stop watching.
Coding agents are writing more of your code and shipping it more often. DeployAngel compares each release with your last healthy one in production and tells you, and your agent, when it's cleared or what broke. That includes what quietly stops, like a scheduled job that skips its run or a webhook that stops arriving.
For Ruby, Python, and .NET apps. Verdicts reach you by Slack, email, or PagerDuty, and reach CI and coding agents like Claude Code and Cursor through a CLI and MCP server.
-
✓ Cleared v381 14:18 · 18 min after rollout
Cleared for normal traffic. Confidence high, coverage 94%.
Still watching
NightlyInvoiceJob, due by 03:00.Changed but not yet exercised:
POST /password_resets -
✕ Failed v382 41 min after rollout
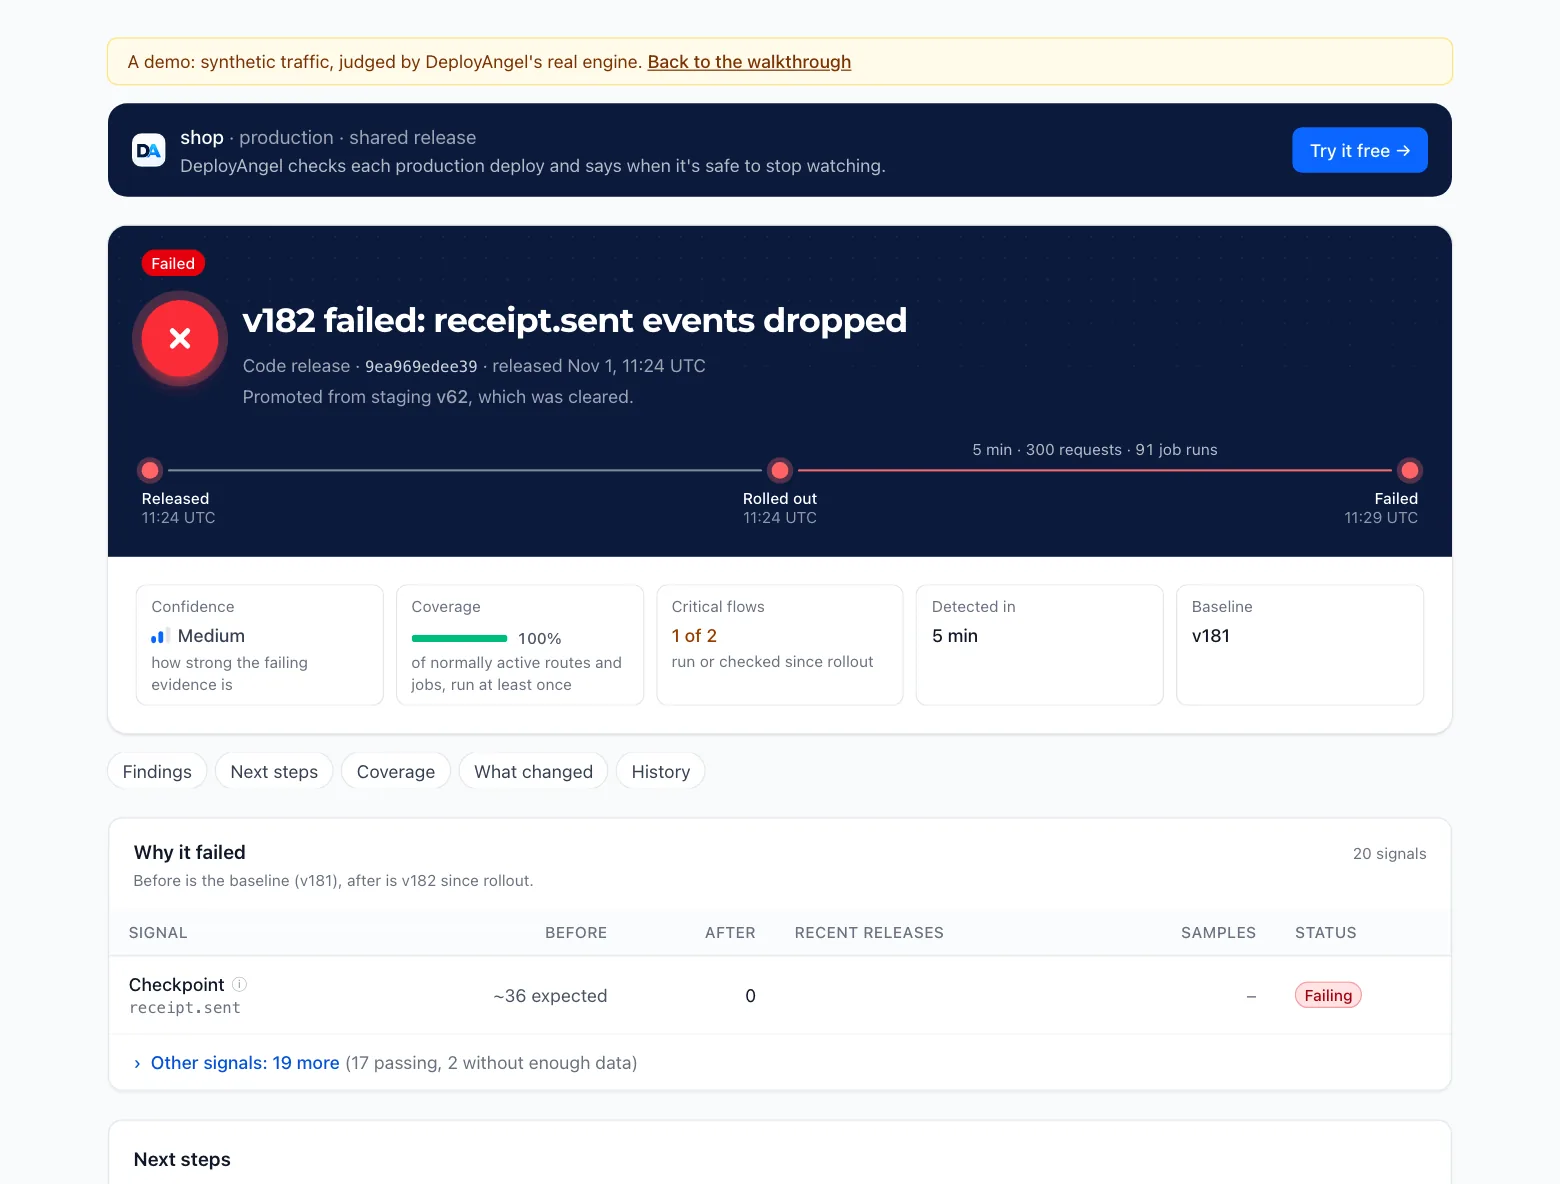
Nothing errored, but receipts stopped:
receipt.sentwent from 38 an hour to 0.Passing: 5xx rate, latency, exceptions
Most relevant change:
app/models/order.rbv381 was the last cleared release.
Why DeployAngel
Ship more often, without watching every deploy
Stop babysitting releases
DeployAngel tells you when a release has seen enough real traffic to be safe, so you can move on.
Let agents check their own work
Your agent or CI waits for the verdict, so a bad release stops the pipeline with the reason attached.
Catch what tests can't
A slower route, a broken checkout, a nightly job that quietly stopped: production shows what tests miss.
Works alongside Sentry and Scout
They show errors and slow requests. DeployAngel decides whether the deploy is fine. More
How it works
From deploy to verdict, no thresholds to tune
-
1
Add the agent
Add the agent for your language and set one token. Most frameworks need one line of setup, and Rails needs none. Or let your coding agent set it up, with a one-time code instead of tokens.
# Ruby: Gemfile
gem "deployangel"

# Python
pip install deployangel

# .NET
dotnet add package DeployAngel
-
2
Deploy as usual
DeployAngel notices each new release on Kamal, Docker, Render, Fly.io, Heroku, or your own servers.
# Optional, after deploying deployangel release -
3
Get a verdict
It compares the release with your last healthy one. Failures alert you right away.
✓ Cleared ✕ Failed ! Not cleared yet
What it catches
Problems a green deploy can hide
Works as soon as the agent reports
- ✓Error rates and latency for every route and job, compared with the last healthy release
- ✓New exceptions, and spikes in existing ones
- ✓Routes and jobs that get far less traffic while nothing errors, like a partner's webhook that stops arriving because of what the release sent it. Checked after each release, and every hour in between, with one alert when it drops and one when it's back. Routes and jobs the release removed don't count.
- ✓Recurring jobs that skip a run, read from your schedules, from Solid Queue to Celery Beat. A run missed after clearance takes the clearance back.
- ✓Rarely used paths like password resets, flagged when they changed but haven't run yet, with an alert if they fail the first time they do
Worth adding for what your business depends on
- +Checkpoints for work that should keep happening, like receipts sent or webhooks processed. Add
DeployAngel.checkpoint("order.created")and a release fails if orders stop, even when every request still returns 200. - +Critical flows like sign-in or checkout, listed on every clearance, and required to run before a release clears if you choose
Rails apps get mail delivered and files stored as checkpoints with nothing to add. Only drops count. A checkpoint without enough everyday activity to compare never keeps a release from clearing.
Points at the cause
A failed release names the affected routes, the new exceptions, and the changed files most likely behind it.
Honest about low traffic
Quiet apps and after-hours deploys wait for normal activity, and the clearance report lists anything that couldn't be observed.
What you get when a release fails
The verdict first, with the signals that failed it and what changed. Then where to roll back to, and for a new exception, which file to open first and the command that prints its stack trace.
AI investigation, if you turn it on, adds an explanation labeled as inference. It never decides the verdict.
Example from DeployAngel's demo app: receipts stopped while every request still succeeded. The traffic is synthetic; the verdict and findings come from the real engine.
Walk through this failure and its fix →
See a real release: one of DeployAngel's own, cleared in production →
 Open the whole page →
Release by release
For teams that deploy all day, and apps that sit quiet
Deploying faster than releases clear?
The next release that clears covers every change since the last cleared one.
- ✓ v184
- v185
- v186
- v187
- ✓ v188 cleared
v185 to v187 were replaced before they could clear. v188 is compared with v184, the last cleared release, so its verdict covers all four.
Cleared doesn't mean forgotten
A release clears once normal traffic has run, but some work only happens later. DeployAngel keeps watching it, and takes the clearance back if it doesn't happen.
- 14:18✓ Clearedv381 cleared for normal traffic. Still watching
NightlyInvoiceJob, due at 03:00. - 03:15✕ Revoked
NightlyInvoiceJobdidn't run. The clearance is revoked, and you're alerted.
No deploy for a while? Jobs that weren't due yet are watched until they run, for up to 8 days, and rarely used paths are checked the first time they run, for up to 30 days.
Features
Everything included
- ✓Cleared, Failed, or Not cleared yet, decided by fixed rules you can read, never by AI
- ✓Compared with your last healthy release, with confidence and coverage on every verdict
- ✓Routes, jobs, exceptions, and checkpoints, each checked on its own
- ✓Alerts by email, Slack, PagerDuty, or signed webhooks, and verdicts in Honeybadger or AppSignal
- ✓A CLI and MCP server, so CI and coding agents can wait for a verdict
- ✓Kamal, Docker, Render, Fly.io, Heroku, and more
$0 while DeployAngel is in beta
- ✓Every feature, all of them
- ✓Unlimited apps, each with staging
- ✓Unlimited teammates
- ✓90 days of release history
- ✓No credit card
- ✓Notice before paid plans start
Built for coding agents
Give your coding agent production feedback
Let your agent implement, deploy, check production, and move on to the next task. DeployAngel keeps watching what hasn't run yet, and tells the agent, or you, the moment something fails.
Through the deployangel MCP server and CLI, with Claude Code, Cursor, Codex, or CI:
- ✓Waits for the verdict after it deploys, and never reports "no problems so far" as cleared
- ✓When a release fails, gets the regressed routes and jobs, new exceptions, and the changes most likely behind them in one call
- ✓Knows what hasn't run since the deploy, like a nightly job or a rarely used page, and can exercise the read-only parts itself
- ✓After a fix, confirms each earlier problem is healthy again, from the new release's own traffic
- ✓Starts each session with what's still open: releases not cleared yet and late regressions
- ✓Read-only tokens: production evidence without database or infrastructure credentials
> Upgrade Rails to 8.1 and make sure
  production is happy.

⏺ Deployed v382. Waiting for the verdict…
  $ deployangel verify --wait
  v382 failed 41 min after rollout
  failing  checkpoint receipt.sent
           38 an hour → 0 since v382
  passing  5xx rate, latency, exceptions
  Next steps:
    v381 was the last cleared release.
    No migration files changed since then.

⏺ Nothing errored, but receipts stopped.
  order.rb changed in this release. Its
  after_commit callback no longer fires
  after the upgrade. Here's a fix. Roll
  back to v381 first?
Safe to install
Requests never wait on DeployAngel's network
Microseconds per requestRecording a request is a few counter updates in memory, about 2 µs. A background thread sends them once a minute; requests never wait on the network.
No request dataRoute patterns, counts, and exceptions with values stripped, or without messages at all if you turn them off. The agent never sends request bodies, parameters, or source code.
Fails openIf DeployAngel is unreachable, your app is unaffected, and the agent holds up to an hour of telemetry to send once it's back.
Questions
Before you install
- Is it really free?
- Yes. During the beta, every feature is free for unlimited apps and teammates, with no credit card. Account owners will hear from us before paid plans start. More about the beta.
- I already use Sentry or Scout. Do I need this?
- Keep them. They show you errors and slow requests, and you decide whether a deploy is fine. DeployAngel decides for you, and catches what never throws an error, like a job that stops running or a webhook that stops arriving. If you deploy rarely and check your dashboards after every release anyway, you may not need it.
- What if a release fails for a change I made on purpose?
- A route or job the release removed isn't held against it. For any other intended drop, like a webhook you switched off, someone on your team can accept the finding as intended on the release page, with a reason. Nothing else failed it? It's verified again, and the releases after it aren't failed for the same change. Coding agents can't accept their own failures: they hand you the link instead.
- What does it need from my app?
- A Ruby, Python, or .NET app on a supported framework, the agent for its language, and one token. For an app's first 24 hours, DeployAngel learns what's normal, so install it a day before a deploy you want cleared. It's built for apps with steady traffic and frequent deploys: at a few hundred requests an hour, a release clears in about 15 minutes with every signal judged. A quiet app still gets a verdict, but it takes longer and rests on less, so run a smoke test after each deploy.
- Is the agent safe to run in production during a beta?
- Yes. Recording a request takes about 2 µs, nothing waits on the network, and memory stays around 4 MB at most. If DeployAngel is unreachable, your app carries on. The agents are open source, benchmark included.
- Do I need to connect GitHub?
- No. Verdicts come from production alone. Connecting GitHub adds pull requests, upgrades, and migrations to each release, ranks the files most likely behind a failure, and shows each verdict as a check on its commit. It reads only the repositories you choose. The privacy policy lists what's shared, including with AI investigation, which is off by default.
Stop watching dashboards after every deploy.
Ruby, Python, and .NET apps, on Kamal, Docker, Render, Fly.io, Heroku, or anywhere they run.